ChainProof
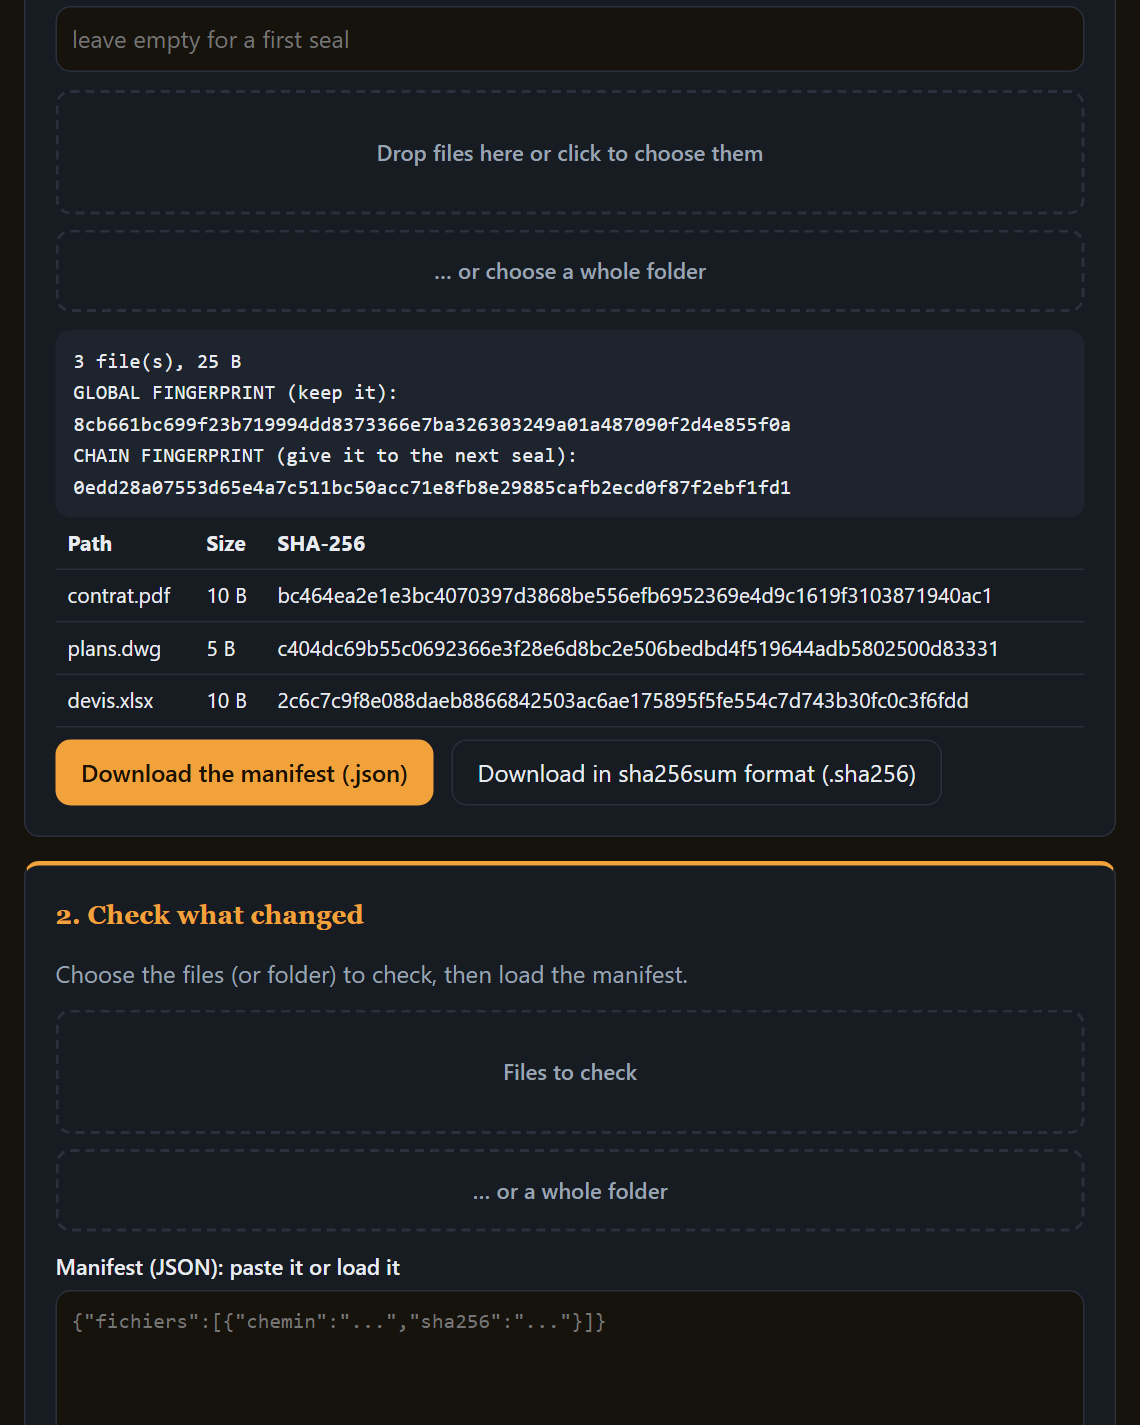
File integritySeals a set of files or a folder: a manifest of fingerprints and an overall fingerprint. Later, it tells you what is identical, modified, missing or added.
Proves integrity, not a legally binding date.
€19See the page →
All tools / WebhookNinja Local
A small Python program that sits in front of your application: it checks every webhook, drops duplicates, keeps everything and retries for as long as your application does not answer.
Stripe signature (with timestamp check), GitHub, Shopify or generic HMAC. A wrong signature is rejected and logged.
Every event is stored in a SQLite file; an event already received is ignored.
Delivered to your application with spaced retries, from 5 seconds to 1 hour. What still fails goes to a dead-letter queue, replayed with one command. Token-protected dashboard.
Because your payment or order events stay with you: no subscription, no quota, no third party seeing your data go by.
You need to run a command and register a URL with the webhook provider. The read-me gives the full example for Stripe.
Soon. Sign up below: one single message when sales open.
Leave your e-mail and the tool you are interested in. One message when sales open, nothing else.
Seals a set of files or a folder: a manifest of fingerprints and an overall fingerprint. Later, it tells you what is identical, modified, missing or added.
Proves integrity, not a legally binding date.
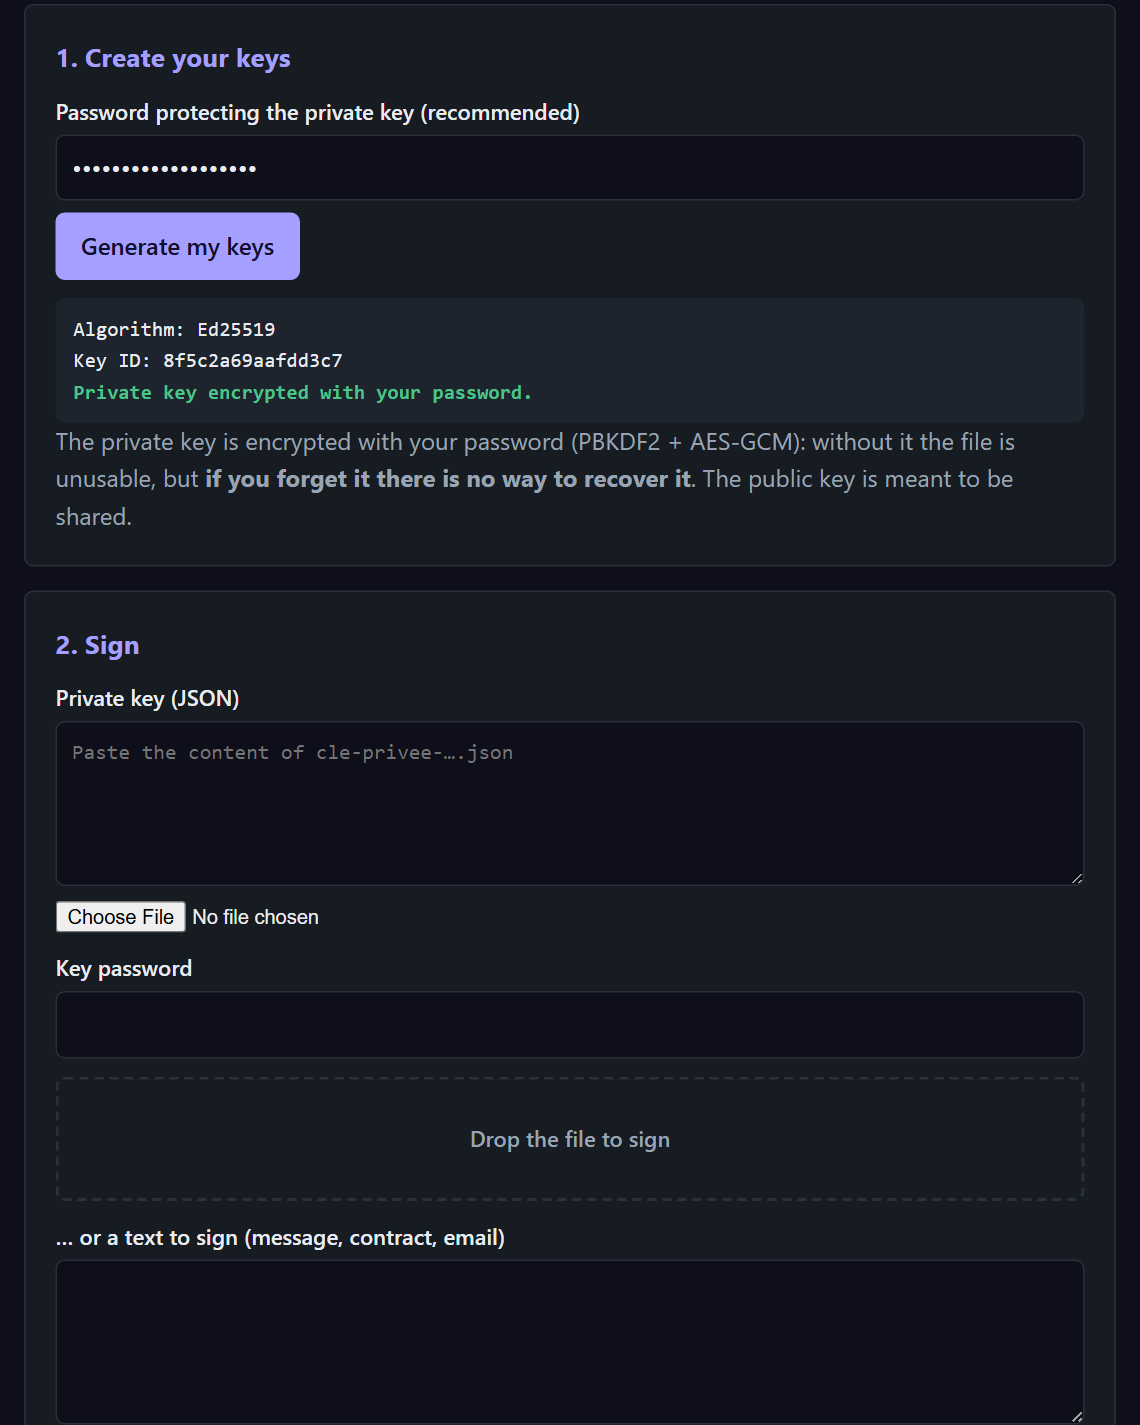
Signs and verifies a file or a text, with keys generated on your machine and a password-protected private key. No command line.
Not a qualified eIDAS signature.
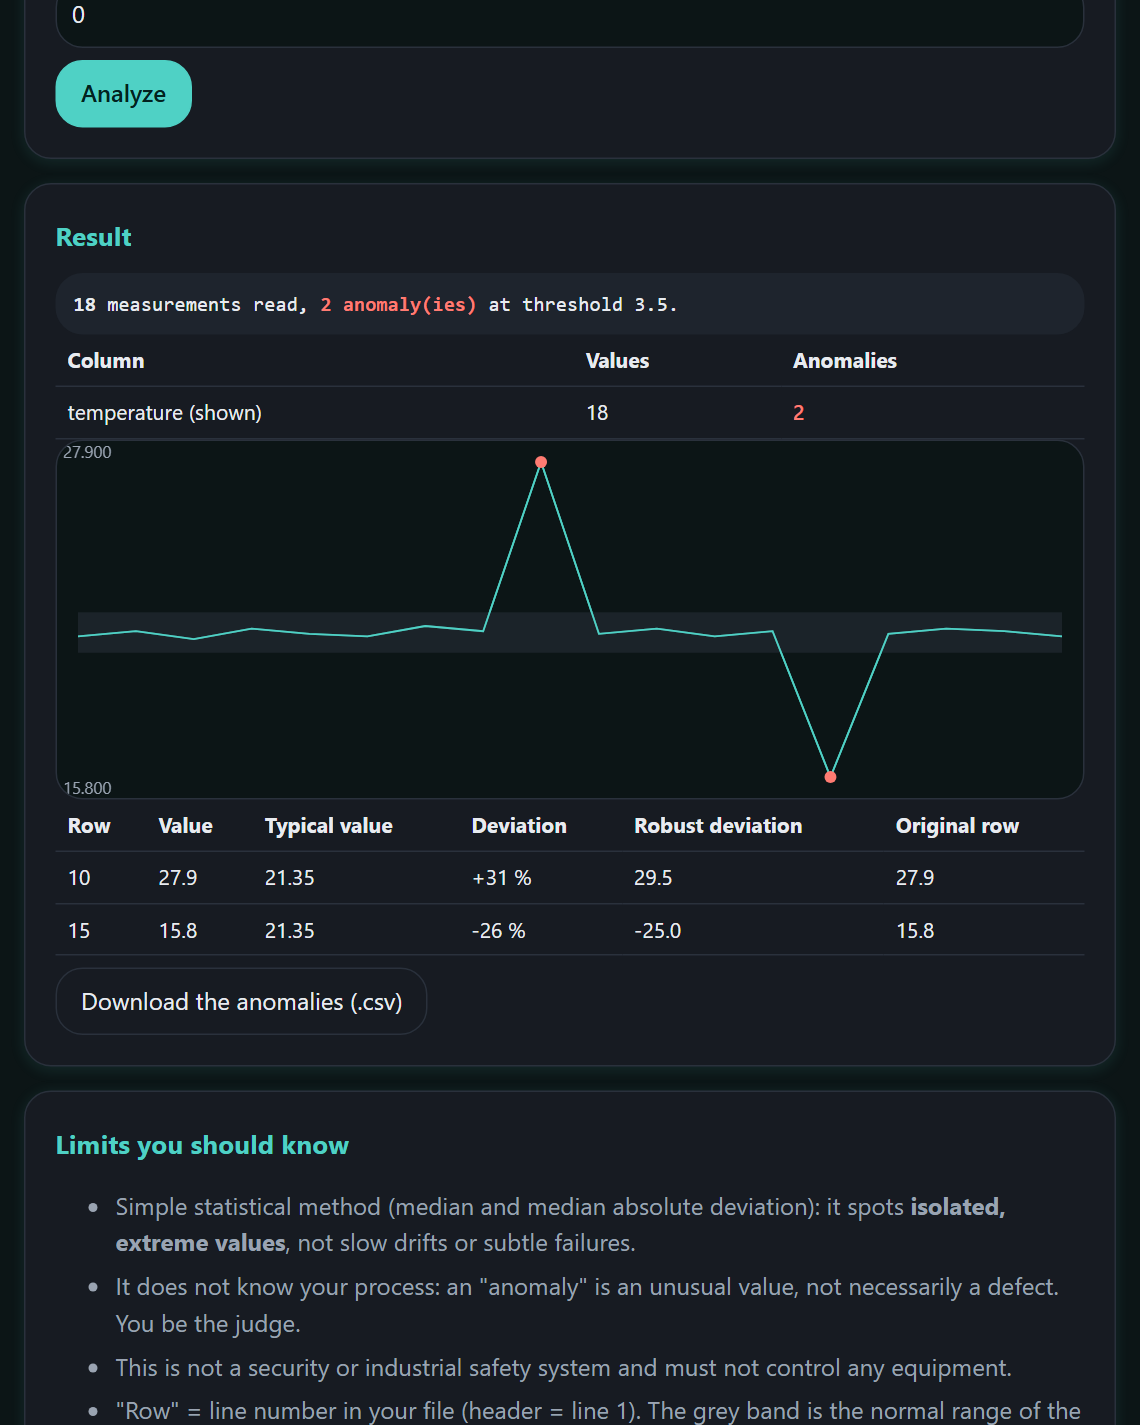
Drop in a CSV file: it spots abnormal values in each column, shows the typical value and the deviation, with a chart.